WiFi Security — WPA3, 802.1X, Rogue AP Detection, Ekahau Site Survey

WiFi Security: WPA3, 802.1X, Rogue AP Detection, and Site Survey

WiFi Security: WPA3, 802.1X, Rogue AP Detection, and Site Survey This article is part of the Enterprise WiFi series. New to enterprise wireless? Start with the overview: Enterprise WiFi Architecture: From Standards to Deployment Why WiFi Security Is Different Wired network security benefits from physical access control — a device must be physically connected to the network to communicate on it. WiFi removes this constraint. Anyone within RF range of your access point can attempt to connect. Your network’s perimeter is literally invisible and extends beyond your walls. ...
April 27, 2026 Â· 12 min Â· Barash Helvadzhaoglu
Cisco ISE Architecture and Licensing Guide

Cisco ISE: Architecture, Licensing, and When to Use It

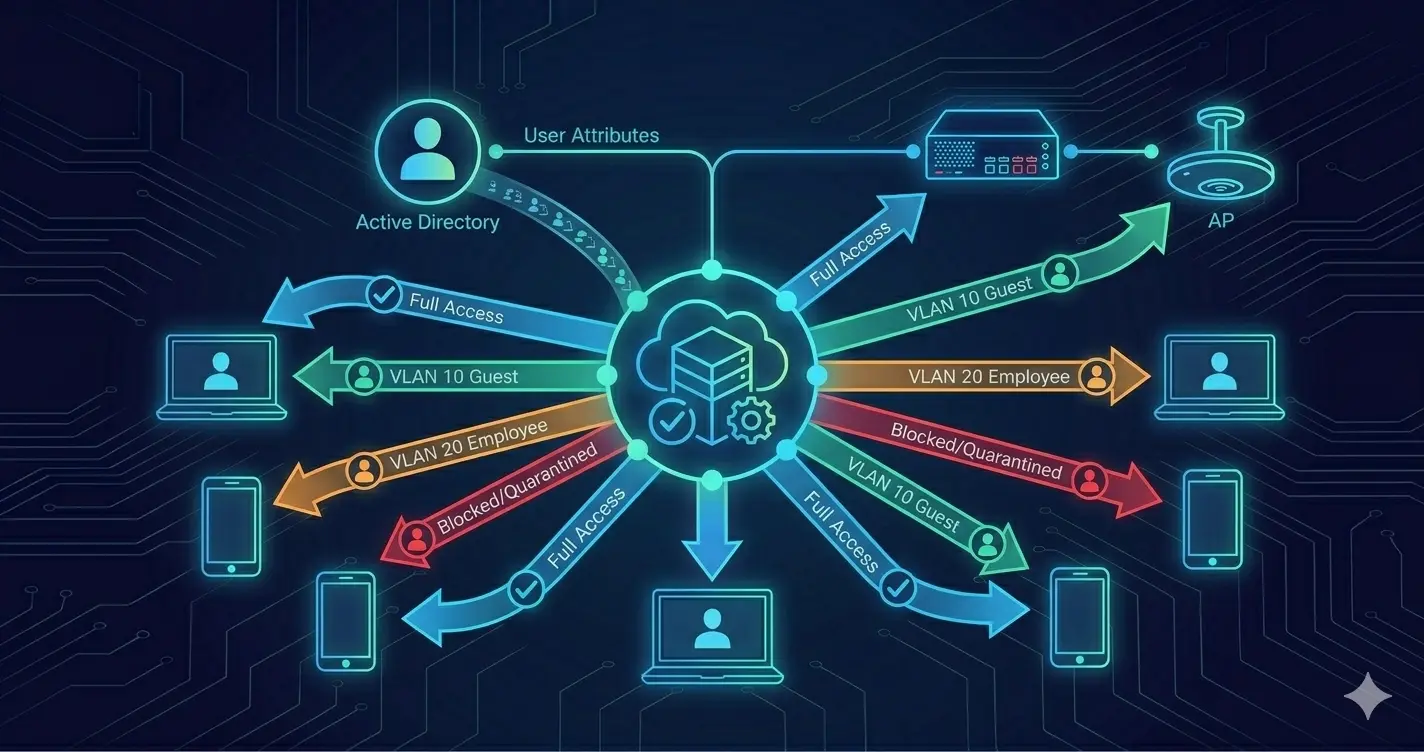
Cisco ISE: Architecture, Licensing, and When to Use It Cisco Identity Services Engine (ISE) is the policy brain behind enterprise network access control. It’s the platform that answers the question — for every device trying to connect to the network — of who are you, what are you, are you healthy, and what are you allowed to do? If you’ve read the 802.1X field guide, you’ve already seen ISE in action: it’s the RADIUS server that returns dynamic VLAN assignments, the NAC platform that profiles devices, the policy engine that enforces posture compliance. This article steps back from the protocol details and looks at ISE as an architectural and investment decision — how it’s structured, how it’s licensed, and when it’s the right tool. ...

April 20, 2026 Â· 9 min Â· Barash Helvadzhaoglu
802.1X Identity-Based Network Access Architecture

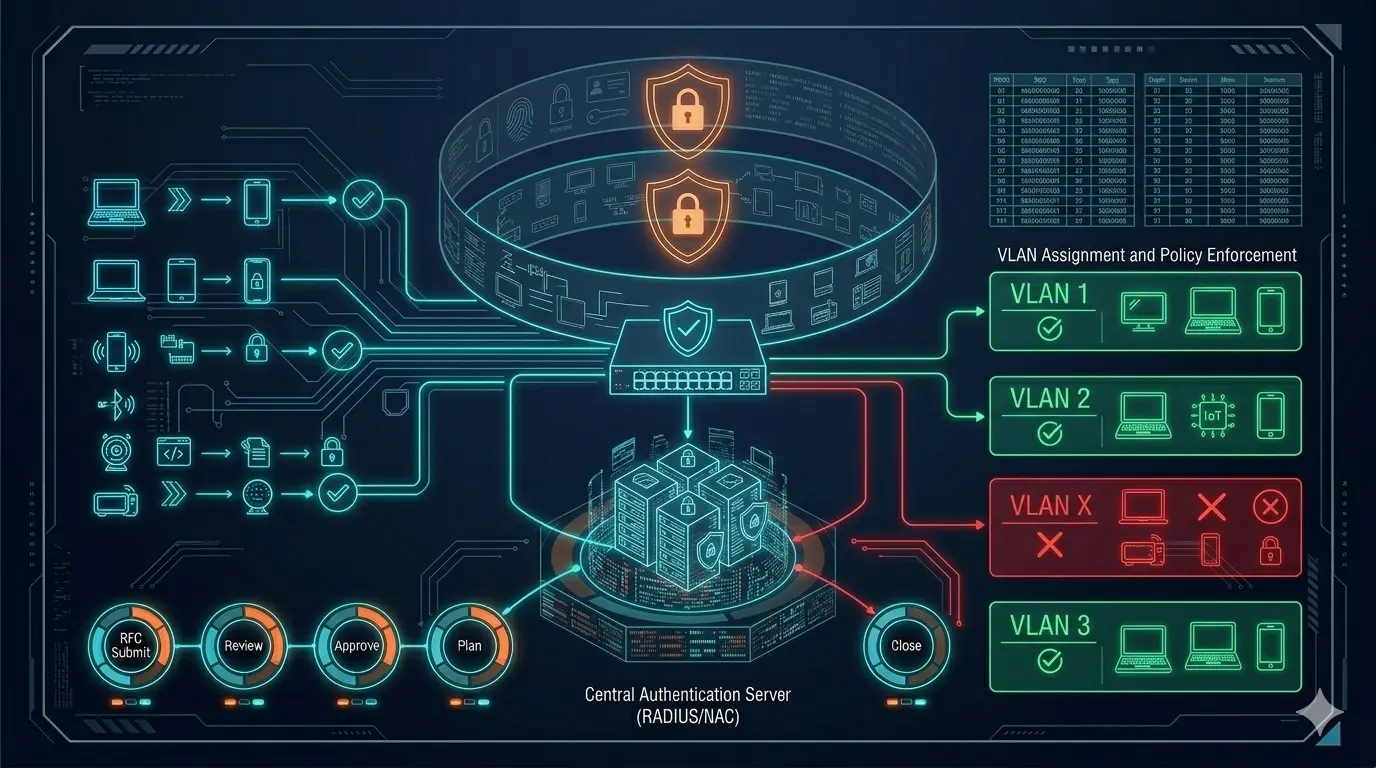
802.1X Projects: Deploying the Identity-Based Architecture in the Field

802.1X Projects: Deploying the Identity-Based Architecture in the Field 802.1X projects look like a network job from the outside; because the points of contact are switch ports, SSIDs, and RADIUS. But in real life, the success of 802.1X is often determined not on the network devices, but in the Active Directory structure, the certificate infrastructure (PKI), and endpoint management. The reason is simple: 802.1X forces the organization to talk about its “identity model” rather than just the port’s VLAN. In other words, you transition from “which port belongs to which VLAN” to a system of “which identity enters the network with what authority.” ...

January 14, 2026 Â· 18 min Â· Barash Helvadzhaoglu
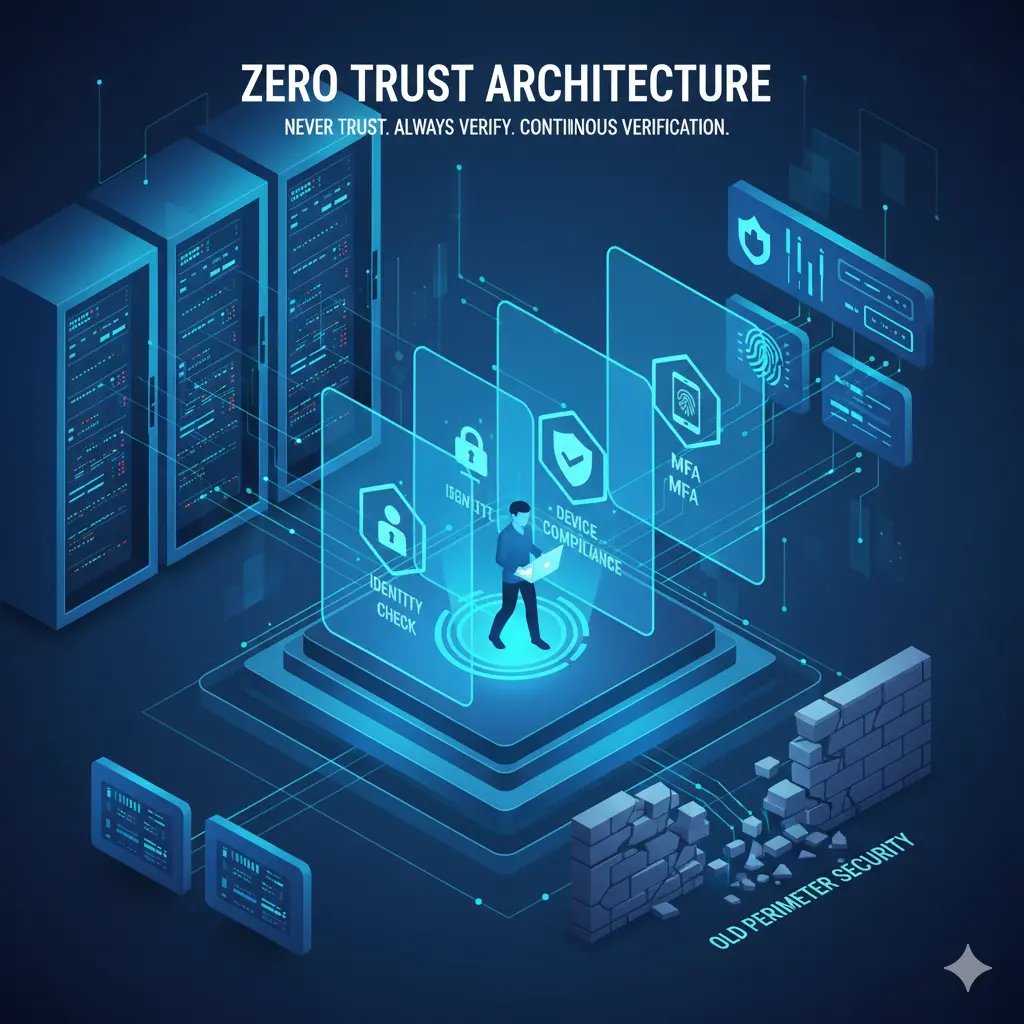
The Zero Trust Mindset: Engineering Security as an Architecture, Not a Product

The Zero Trust Mindset: Engineering Security as an Architecture, Not a Product

The Zero Trust Mindset: Engineering Security as an Architecture, Not a Product Zero Trust is a concept mentioned in almost every security presentation today. However, when we look at its implementation in the field, we often see it applied in the wrong place, with wrong expectations, and using the wrong tools. The main reason for this is that Zero Trust is positioned as a technology or a purchasable product. In reality, Zero Trust is not a licensed, boxed, or vendor-specific solution. It is an architectural perspective and, more importantly, a mindset. ...

January 3, 2026 Â· 7 min Â· Barash Helvadzhaoglu